VPC Network Architecture
Design secure, scalable VPC architectures with proper subnet segmentation and network controls.
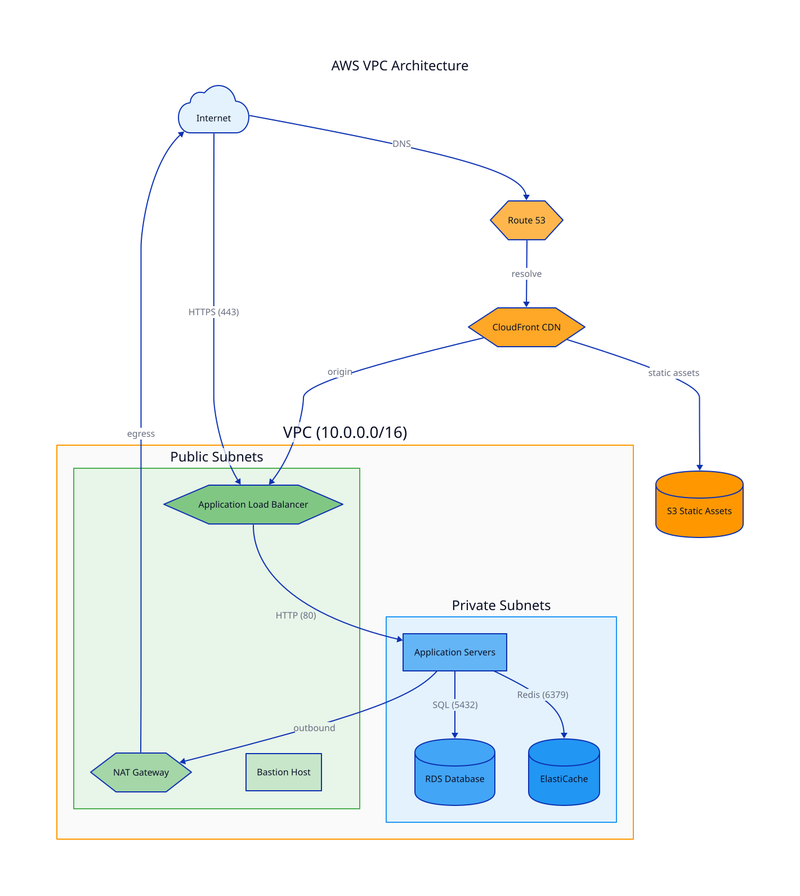
VPC architecture with public and private subnets across availability zones
A well-designed VPC (Virtual Private Cloud) is the foundation of your AWS infrastructure. It provides network isolation, security controls, and connectivity options that support both simple applications and complex multi-tier architectures.
Our VPC designs typically include:
- Public Subnets - For load balancers, NAT gateways, and bastion hosts
- Private Subnets - For application servers, databases, and internal services
- Network ACLs & Security Groups - Defense in depth with stateless and stateful firewalls
- VPC Peering & Transit Gateway - Inter-VPC connectivity for multi-account architectures
Key Concepts
- Multi-AZ deployment for high availability
- Proper CIDR planning to avoid conflicts
- NAT Gateway for secure outbound connectivity
- VPC Flow Logs for network monitoring
- Private Link for AWS service access without internet exposure